Code: 36579979
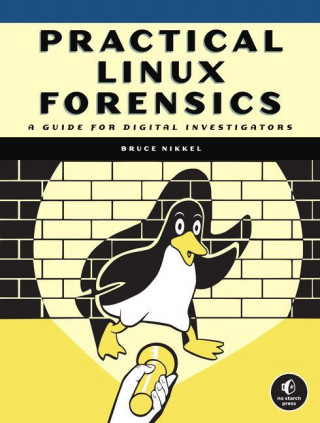
Practical Linux Forensics
by Bruce Nikkel
A resource to help forensic investigators locate, analyze, and understand digital evidence found on modern Linux systems after a crime, security incident or cyber attack.Practical Linux Forensics dives into the technical details o ... more


- Language:
 English
- Binding: Paperback
- Number of pages: 400
Publisher: No Starch Press,US, 2021
- More about this

39.25 €
RRP: 60.17 €
You save 20.92 €

In stock at our supplier
Shipping in 3 - 6 days
You might also like
-
Threshing Day (Wing and Claw Collection)
17.96 € -29 % -
Berserk Deluxe Volume 1
38.95 € -27 % -
Berserk Deluxe Volume 3
55.32 € -

Vagabond Definitive Edition, Vol. 5
38.65 € -29 % -

Nightwing: Leaping Into the Light
10.43 € -2 % -

Birthday Girl
14.35 € -20 % -

Strangers
17.16 € -23 % -
Caught Up
10.63 € -21 % -

Monster: The Perfect Edition, Vol. 3
20.17 € -11 % -
Akira 35th Anniversary Box Set
149.90 € -28 % -
My Friends
12.24 € -
Ghost in the Shell: Fully Compiled
46.58 € -13 % -

The Intelligent Investor
20.88 € -15 % -
Chainsaw Man, Vol. 2
10.13 € -43 % -
Anne of Green Gables, Complete 8-Book Box Set
47.48 € -26 % -
How Linux Works, 3rd Edition
35.43 € -29 % -

The Fourth Turning Is Here
13.75 € -25 % -
Linux Basics for Hackers, 2nd Edition
28.71 € -29 % -

Adventure Time Compendium Vol. 1
45.38 € -5 % -
Refactoring
53.91 € -17 % -
Open Circuits
28.11 € -29 % -

Game Programming Patterns
36.04 € -7 % -

The Lord of the Rings
259.25 € -24 % -
Penetration Testing
36.14 € -25 % -
Elixir in Action, Third Edition
57.53 € -10 % -

Pokecology: An Illustrated Guide to Pokemon Ecology
15.85 € -25 % -

Three Waves of Volunteers and the New Earth
13.65 € -25 % -

Monstress Book One
36.14 € -25 % -

Monstress Book Two
43.27 € -30 % -

The Game Master's Box of Unlimited Adventure
42.16 € -33 % -

Adventure Time: The Fionna and Cake Compendium
24.19 € -24 % -

Hobbit
125.10 € -24 % -
Death and Life of Great American Cities
17.06 € -18 % -

Pokemon Adventures FireRed & LeafGreen / Emerald Box Set : Includes Vols. 23-29
53.81 € -27 % -
Bare Metal Computing X64 Edition
32.62 € -7 % -
Slayers Volumes 13-15 Collector's Edition
29.01 € -20 % -

Learning eBPF
40.36 € -25 % -

Chip War: The Fight for the World's Most Critical Technology
15.75 € -25 % -
Slayers Volumes 10-12 Collector's Edition
25.70 € -22 % -

Tcp/ip Guide
70.28 € -29 % -

How to Win an Information War
11.64 € -21 % -
Practical Doomsday
18.87 € -25 % -
Practical Binary Analysis
41.96 € -29 % -
Clean Agile
39.45 € -10 % -
Understanding the Linux Kernel 3e
48.89 € -24 % -
Mastering Blockchain - Fourth Edition
45.98 € -2 % -
Serious Python
28.11 € -29 % -
C++ Crash Course
40.96 € -31 % -
Mastering KVM Virtualization
53.21 € -1 % -
Linux Bible, Tenth Edition
44.87 € -23 % -
Kali Linux Penetration Testing Bible
30.51 € -25 % -
Hacking Apis
42.26 € -29 % -
Ghidra Book
40.25 € -30 % -

Effective Rust
42.06 € -24 % -

Practical Forensic Imaging
39.15 € -19 % -
Mastering Docker
42.46 € -1 % -
Linux
43.17 € -24 % -
Mastering Linux Security and Hardening - Third Edition
46 € -2 % -
How Cybersecurity Really Works
28.51 € -29 % -
UNIX and Linux System Administration Handbook
112.55 € -

Invent Your Own Computer Games With Python, 4e
28.51 € -29 % -
Hardware Hacking Handbook
42.26 € -29 % -
Poc || Gtfo
28.81 € -27 % -
Practical Social Engineering
24.99 € -30 % -
Practical Iot Hacking
52.60 € -29 % -

Appleseed Alpha
22.18 € -29 % -
Rule 34
6.12 € -29 % -

Linux Kernel in a Nutshell
24.99 € -24 % -
Linux Basics For Hackers
39.65 € -25 % -

Game Engine Architecture, Third Edition
129.57 € -

CompTIA Security+ All-in-One Exam Guide, Sixth Edition (Exam SY0-601))
64.25 € -
Ethical Hacking
33.73 € -31 % -
CCNA Security 210-260 Official Cert Guide
50.09 € -
Tallinn Manual 2.0 on the International Law Applicable to Cyber Operations
73.69 € -2 % -
Black Hat Go
34.53 € -29 % -
Rootkits And Bootkits
35.43 € -29 % -

Arduino Workshop
25.19 € -24 % -

Linux for Beginners: An Introduction to the Linux Operating System and Command Line
22.49 € -6 % -

Bare Metal C
32.82 € -32 % -

Practical Linux System Administration: A Guide to Installation, Configuration, and Management
55.72 € -25 % -
Designing Secure Software
36.24 € -25 % -

Woman with the Ring
11.64 € -7 % -

Unfinished Tales
103.91 € -24 % -

Cadaver Dog Handbook
107.83 €
Give this book as a present today
- Order book and choose Gift Order.
- We will send you book gift voucher at once. You can give it out to anyone.
- Book will be send to donee, nothing more to care about.
More about Practical Linux Forensics
You get 96 loyalty points
 Book synopsis

A resource to help forensic investigators locate, analyze, and understand digital evidence found on modern Linux systems after a crime, security incident or cyber attack.Practical Linux Forensics dives into the technical details of analyzing postmortem forensic images of Linux systems which have been misused, abused, or the target of malicious attacks. It helps forensic investigators locate and analyze digital evidence found on Linux desktops, servers, and IoT devices. Throughout the book, you learn how to identify digital artifacts which may be of interest to an investigation, draw logical conclusions, and reconstruct past activity from incidents. You ll learn how Linux works from a digital forensics and investigation perspective, and how to interpret evidence from Linux environments. The techniques shown are intended to be independent of the forensic analysis platforms and tools used.Learn how to: Extract evidence from storage devices and analyze partition tables, volume managers, popular Linux filesystems (Ext4, Btrfs, and Xfs), and encryption Investigate evidence from Linux logs, including traditional syslog, the systemd journal, kernel and audit logs, and logs from daemons and applications Reconstruct the Linux startup process, from boot loaders (UEFI and Grub) and kernel initialization, to systemd unit files and targets leading up to a graphical login Perform analysis of power, temperature, and the physical environment of a Linux machine, and find evidence of sleep, hibernation, shutdowns, reboots, and crashes Examine installed software, including distro installers, package formats, and package management systems from Debian, Fedora, SUSE, Arch, and other distros Perform analysis of time and Locale settings, internationalization including language and keyboard settings, and geolocation on a Linux system Reconstruct user login sessions (shell, X11 and Wayland), desktops (Gnome, KDE, and others) and analyze keyrings, wallets, trash cans, clipboards, thumbnails, recent files and other desktop artifacts Analyze network configuration, including interfaces, addresses, network managers, DNS, wireless artifacts (Wi-Fi, Bluetooth, WWAN), VPNs (including WireGuard), firewalls, and proxy settings Identify traces of attached peripheral devices (PCI, USB, Thunderbolt, Bluetooth) including external storage, cameras, and mobiles, and reconstruct printing and scanning activity
Book details
Book category Books in German Naturwissenschaften, Medizin, Informatik, Technik Informatik, EDV Betriebssysteme, Benutzeroberflächen
39.25 €
- Full title: Practical Linux Forensics
- Author: Bruce Nikkel
- Language: English
- Binding: Paperback
- Number of pages: 400
- EAN: 9781718501966
- ISBN: 171850196X
- ID: 36579979
- Publisher: No Starch Press,US
- Weight: 746 g
- Dimensions: 232 × 179 × 324 mm
- Date of publishing: 21. December 2021
Trending among others
-

Linux Shell Scripting
18.16 € -7 % -
Mastering Windows Server 2025 - Fifth Edition
48.09 € -1 % -
Operating System Concepts
102.61 € -
CompTIA A+ Complete Study Guide
45.17 € -26 % -
The awk Programming Language
35.03 € -14 % -
Hands-On Design Patterns with C++ - Second Edition
46.88 € -2 % -
Windows Server 2025 Administration Fundamentals - Fourth Edition
46.28 € -1 % -
Windows 11 Mastery
32.62 € -
Red Hat RHCE 8 (EX294) Cert Guide
31.82 € -24 % -
The Ultimate Kali Linux Book - Third Edition
51.80 € -2 % -
Ubuntu 24.04 LTS Desktop
41.86 € -1 % -
Building Low Latency Applications with C++
41.56 € -1 % -

Mastering Swift 6 - Seventh Edition
41.56 € -1 % -

Mastering Microsoft Intune - Second Edition
50.50 € -1 % -

End-to-End Automation with Kubernetes and Crossplane
50.52 € -1 % -
CompTIA A+ Certification All-in-One Exam Guide, Eleventh Edition (Exams 220-1101 & 220-1102)
41.56 € -25 % -
Linux All-in-One For Dummies, 7th Edition
29.31 € -25 % -
RHCSA Red Hat Enterprise Linux 10
53.51 € -7 % -
Microsoft Power Bi Step by Step
43.87 € -14 % -
Exam Ref AZ-900 Microsoft Azure Fundamentals
29.11 € -25 % -
Product Operations
24.29 € -2 % -
Book Of Kubernetes
40.25 € -30 % -
Linux Kernel Programming - Second Edition
47.28 € -1 % -
Exam Ref AZ-305 Designing Microsoft Azure Infrastructure Solutions
36.84 € -14 % -
Mastering Ubuntu Server - Fourth Edition
51.50 € -2 % -
101 Best Excel Tips & Tricks
32.42 € -
RHCSA Red Hat Enterprise Linux 9
41.96 € -7 % -
The Kubernetes Bible - Second Edition
54.91 € -2 % -
Mastering Embedded Linux Development - Fourth Edition
45.98 € -2 % -
Learning Microsoft Intune
13.45 € -2 % -
101 Most Popular Excel Formulas
32.42 € -
The Ultimate Power Query Cookbook for Power BI and Excel
30.51 € -19 % -
Mastering Windows Security and Hardening - Second Edition
51.50 € -
Excel 2021
23.69 € -23 % -
The Atomic Habits
16.16 € -1 % -
Microservices Design Patterns in .NET - Second Edition
45.98 € -2 % -
Linux
11.24 € -25 % -
PowerShell 4.0 für die Windows-Administration
42.26 € -6 % -
The Software Developer's Guide to Linux
38.85 € -2 % -
Linux Pocket Guide
22.08 € -25 % -
Optimizing DAX
62.95 € -2 % -
iPhone 6s und 6s Plus
1.80 € -91 % -
Well-Grounded Java Developer, The
62.04 € -5 % -
Windows 11
18.87 € -5 % -
Exam Ref AZ-500 Microsoft Azure Security Technologies, 2/e
36.84 € -14 % -
Mastering Windows Server 2022 - Fourth Edition
81.72 € -2 % -
Retro - Spiele Katalog Gameboy
7.62 € -

Windows 11 in easy steps
13.65 € -19 % -
Command-Line Rust
46.08 € -25 %
Collection points Bratislava a 13504 dalších
Copyright ©2008-26 najlacnejsie-knihy.sk All rights reservedPrivacyCookies

 27012 collection points
 Delivery 2.99 €
 02/210 210 99 (8-15.30h)
