Code: 54566981
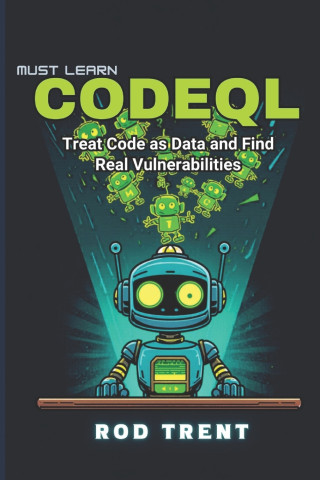
Must Learn CodeQL
by Rod Trent
Stop chasing the same bug twice. Learn to treat your code as data.CodeQL is the semantic code analysis engine behind GitHub code scanning. Pattern-matching scanners search for text that looks dangerous. CodeQL turns your code into ... more


- Language:
 English
- Binding: Paperback
- Number of pages: 118
Publisher: Independently published, 2026
- More about this


You might also like
-
Cozy Countdown: An Advent Coloring Book Bundle
21.99 € -25 % -
Threshing Day (Limited Deluxe Edition)
20.99 € -29 % -
Court of Thorns and Roses 6
18.09 € -24 % -
Murdoku
14.29 € -25 % -
White Nights
3.49 € -9 % -

A Conspiracy of Charming Monsters
12.19 € -29 % -

A Conspiracy of Charming Monsters
18.59 € -18 % -
The End of Everything
12.09 € -30 % -
Once Upon a Broken Heart Collector's Edition
27.08 € -29 % -
I'll Believe in Anything. The Making of Heated Rivalry Season 1
18.59 € -30 % -
Berserk Deluxe Volume 1
47.18 € -10 % -
Trust Fall
9.99 € -29 % -
Protocols
11.19 € -31 % -
Jojo's Bizarre Adventure: Part 7--Steel Ball Run, Vol. 9
19.39 € -21 % -

Chainsaw Man, Vol. 22
10.99 € -
The Mirror of Infinite Endings
17.89 € -17 % -
Murdoku Volume 2: Back in Time
14.29 € -25 % -
The Long-Lived King: An Original The Owl House Graphic Novel
19.79 € -15 % -

Witch Hat Atelier: Grimoire Edition 3
36.68 € -23 % -
21 Days of Fear
16.89 € -28 % -
Threshing Day (Wing and Claw Collection)
18.49 € -25 %
Give this book as a present today
- Order book and choose Gift Order.
- We will send you book gift voucher at once. You can give it out to anyone.
- Book will be send to donee, nothing more to care about.
More about Must Learn CodeQL
You get 18 loyalty points
 Book synopsis

Stop chasing the same bug twice. Learn to treat your code as data.
CodeQL is the semantic code analysis engine behind GitHub code scanning. Pattern-matching scanners search for text that looks dangerous. CodeQL turns your code into a database you can query. You can then ask precise questions: Where does untrusted input end up? Which calls reach this sensitive operation? Where else in the codebase is this same bug hiding?
Must Learn CodeQL takes you from installing the tools to writing queries that find real vulnerabilities. Along the way you'll:
- Set up the CodeQL CLI and VS Code extension and build your first database
- Understand what's inside a CodeQL database for interpreted and compiled languages
- Learn the QL language: predicates, classes, modules, recursion, and aggregates
- Write custom predicates and complete queries with proper metadata
- Explore codebases with the standard language libraries
- Track data with data flow analysis, taint tracking, and path queries
- Extend the libraries with your own sources, sinks, and flow models
- Package and ship your work with query packs and suites
- Add CodeQL to GitHub Actions, other CI systems, and multi-repository variant analysis
- Tune query performance and debug flow that stops where it shouldn't
- Turn one known vulnerability into a search that finds all of its variants
Each chapter builds on the last. The examples come from a free companion repository on GitHub, so you can run them as you read.
This book is for security engineers, developers, and anyone who wants to know what code scanning is really doing behind those pull request alerts.
From Rod Trent, author of the Must Learn KQL series.
Book details
7.29 €
- Full title: Must Learn CodeQL
- Author: Rod Trent
- Language: English
- Binding: Paperback
- Number of pages: 118
- EAN: 9798143628601
- ID: 54566981
- Publisher: Independently published
- Weight: 170 g
- Dimensions: 229 × 152 × 6 mm
- Date of publishing: 17. November 2026
Osobný odber Bratislava a 13046 dalších
Copyright ©2008-26 najlacnejsie-knihy.sk Všetky práva vyhradenéSúkromieCookies

 25 miliónov titulov
 Vrátenie do mesiaca
 02/210 210 99 (8-15.30h)
