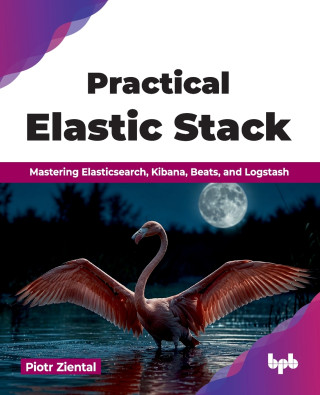
Code: 53868212
Practical Elastic Stack
by Piotr Ziental
Every device in a network, from routers to applications and IoT devices, produces large volumes of logs, metrics, and traces. Commercial observability systems can process this, but they often mean long contracts, higher costs, and ... more


- Language:
 English
- Binding: Paperback
- Number of pages: 436
Publisher: BPB Publications, 2026
- More about this

36.47 €
RRP: 40.59 €
You save 4.13 €

You might also like
-
Threshing Day (Wing and Claw Collection)
17.72 € -29 % -
Threshing Day (Limited Deluxe Edition)
20.95 € -29 % -
Berserk Deluxe Volume 1
38.88 € -25 % -
What Happened Yesterday
15.61 € -27 % -
White Nights
4.52 € -14 % -
Murdoku
14.60 € -22 % -
Berserk Deluxe Volume 2
36.47 € -30 % -
Berserk Deluxe Volume 3
55.51 € -
Court of Thorns and Roses 6
15.51 € -31 % -
Jojo's Bizarre Adventure: Part 7--Steel Ball Run, Vol. 8
18.13 € -25 % -
21 Days of Fear
16.31 € -27 % -
Onyx Storm (Deluxe Limited Edition) (The Empyrean, 3)
24.27 € -24 % -
Yesteryear
16.11 € -21 % -
Dancing The Dream
21.65 € -24 % -
Kid's Box New Generation Level 2 Activity Book with Digital Pack British English
10.77 € -9 % -
The Courage To Be Disliked
10.67 € -13 % -
Kid's Box New Generation Level 3 Activity Book with Digital Pack British English
11.17 € -5 % -
Murdoku
17.02 € -29 % -
Kid's Box New Generation Level 1 Activity Book with Digital Pack British English
11.17 € -5 % -
Witch Hat Atelier: Grimoire Edition 1
43.22 € -30 % -
The Count of Monte Cristo
13.79 €
Give this book as a present today
- Order book and choose Gift Order.
- We will send you book gift voucher at once. You can give it out to anyone.
- Book will be send to donee, nothing more to care about.
Availability alert
Enter your e-mail address and once book will be available,
we will send you a message. It's that simple.
More about Practical Elastic Stack
You get 89 loyalty points
 Book synopsis

Every device in a network, from routers to applications and IoT devices, produces large volumes of logs, metrics, and traces. Commercial observability systems can process this, but they often mean long contracts, higher costs, and sensitive data leaving the company. The Elastic Stack is the leading open-source solution for log management, system security, and enterprise observability. Practical Elastic Stack is your hands-on guide to mastering this powerful technology, designed to help you transform raw log data and security events into actionable operational intelligence.
Beginning with foundational concepts and hands-on installation, this practical guide walks through core architectural concepts, installation methods, and cluster setup across Linux, Windows, and Docker. You will master data transformation pipelines using Logstash, visualize live data, and build interactive dashboards in Kibana. It also covers agent management with Elastic Fleet, application monitoring with APM, and security monitoring with SIEM, with event correlation and detection rules in Kibana. You will learn to leverage the stack for security threat monitoring and set up automated alerting.
By the end of this book, readers will know what distinguishes monitoring from observability and how to build a scalable platform on their network. Upon completing this practical guide, readers possess the real-world skills to design, deploy, and optimize production-ready Elastic Stack environments to solve complex monitoring and security challenges.
WHAT YOU WILL LEARN
● Parse logs from any source into structured ECS documents.
● Build Kibana dashboards to explore and visualize data.
● Manage Beats agents centrally through Elastic Fleet.
● Detect security threats by correlating events in Kibana.
● Forecast trends and spot anomalies with machine learning.
WHO THIS BOOK IS FOR
This book is written for students, DevOps engineers, SREs, security analysts, system administrators, and software developers building in-house observability. Basic familiarity with Linux administration, networking concepts, and Docker containers is helpful, but no prior experience with the Elastic Stack is required.
Book details
36.47 €
- Full title: Practical Elastic Stack
- Subtitle: Mastering Elasticsearch, Kibana, Beats, and Logstash (English Edition)
- Author: Piotr Ziental
- Language: English
- Binding: Paperback
- Number of pages: 436
- EAN: 9789378547959
- ISBN: 9378547958
- ID: 53868212
- Publisher: BPB Publications
- Weight: 746 g
- Dimensions: 235 × 191 × 22 mm
- Date of publishing: 11. September 2026
Osobný odber Bratislava a 13128 dalších
Copyright ©2008-26 najlacnejsie-knihy.sk Všetky práva vyhradenéSúkromieCookies

 25 miliónov titulov
 Vrátenie do mesiaca
 02/210 210 99 (8-15.30h)
