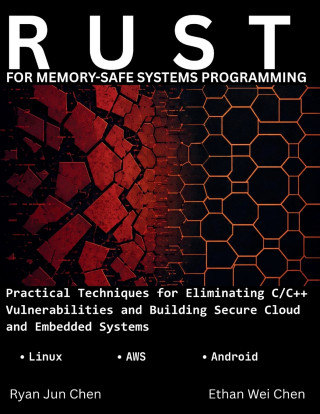
Code: 54075270
RUST FOR MEMORY-SAFE SYSTEMS PROGRAMMING
by Ethan Wei Chen, Ryan Jun Chen
Your C/C++ code has a bug in it right now. You just haven't crashed yet.Buffer overflows, Use-after-free, Dangling pointers. These aren't edge cases, they're the single largest root cause of critical security vulnerabilities in pr ... more


- Language:
 English
- Binding: Paperback
- Number of pages: 286
Publisher: Independently published, 2026
- More about this

29.13 €
RRP: 31.27 €
You save 2.14 €

In stock at our supplier
Shipping in 10 - 16 days
You might also like
-
Threshing Day (Limited Deluxe Edition)
20.62 € -29 % -
Threshing Day (Wing and Claw Collection)
17.92 € -29 % -
Murdoku
14.91 € -21 % -
The Mirror of Infinite Endings
14.61 € -31 % -
The Art of Gravity Falls
36.84 € -31 % -
The Long-Lived King: An Original The Owl House Graphic Novel
16.21 € -30 % -
White Nights
4.50 € -14 % -
Berserk Deluxe Volume 1
38.95 € -27 % -
21 Days of Fear
16.61 € -27 % -
Court of Thorns and Roses 6
15.61 € -30 % -
Onyx Storm (Deluxe Limited Edition) (The Empyrean, 3)
24.22 € -26 % -
Lord of Mysteries, Vol. 4: The Faceless, Part I
16.91 € -15 % -
The Mirror of Infinite Endings
19.12 € -37 % -
Berserk Deluxe Volume 3
55.37 € -
Berserk Deluxe Volume 2
36.54 € -31 % -
Witch Hat Atelier: Grimoire Edition 1
35.14 € -29 % -
Fourth Wing
23.82 € -26 % -
Iron Flame
24.83 € -22 % -
Jojo's Bizarre Adventure: Part 7--Steel Ball Run, Vol. 9
19.12 € -22 % -
Protocols
14.31 € -29 % -
The Courage To Be Disliked
10.60 € -13 %
Give this book as a present today
- Order book and choose Gift Order.
- We will send you book gift voucher at once. You can give it out to anyone.
- Book will be send to donee, nothing more to care about.
More about RUST FOR MEMORY-SAFE SYSTEMS PROGRAMMING
You get 71 loyalty points
 Book synopsis

Your C/C++ code has a bug in it right now. You just haven't crashed yet.
Buffer overflows, Use-after-free, Dangling pointers. These aren't edge cases, they're the single largest root cause of critical security vulnerabilities in production software today, and they're the reason CISA and the NSA have told every software manufacturer in the country to have a memory-safety roadmap in place. If you write systems code in C or C++, that roadmap starts with you.
This book is your roadmap.
Rust for Memory-Safe Systems Programming doesn't teach Rust as an abstract language exercise. It follows one real project, SentinelGuard; a security telemetry platform, from an empty directory to a working system running as a Linux daemon, a cloud service on AWS, firmware on a microcontroller, and a library inside an Android app. Every chapter builds on the last. Every code sample actually compiles and runs, and where something couldn't be verified live (real AWS infrastructure, physical hardware), the book tells you so plainly, instead of pretending.
You'll walk away able to:
- Eliminate the exact bug classes; buffer overflows, use-after-free, data races, that make C and C++ a compliance liability
- Migrate a legacy C/C++ codebase incrementally, without betting your team's roadmap on a risky full rewrite
- Generate real SBOMs and license-compliance reports with cargo-deny and cargo-cyclonedx, and map them directly to CISA's published guidance
- Ship Rust across every surface that matters, Linux daemons, AWS Lambda and DynamoDB, no_std embedded firmware, and Android via JNI/UniFFI, from one shared, tested codebase
- Fuzz, test, and verify your code the way a production security team actually does it, not the way a tutorial pretends to
Whether you're an engineering lead staring down a memory-safety mandate, a C/C++ developer future-proofing your career, or a security engineer who needs to actually understand what a clean cargo-audit run does and doesn't prove, this book was built for the exact moment you're in right now.
The migration to memory-safe systems programming isn't coming. It's already the industry's default. Get ahead of it.
Book details
29.13 €
- Full title: RUST FOR MEMORY-SAFE SYSTEMS PROGRAMMING
- Subtitle: Practical Techniques to Eliminating C/C++ Vulnerabilities, Building Secure and Compliant Kernels, Cloud, and Embedded Systems for Linux, AWS, and Android
- Author: Ethan Wei Chen, Ryan Jun Chen
- Language: English
- Binding: Paperback
- Number of pages: 286
- EAN: 9798178805671
- ID: 54075270
- Publisher: Independently published
- Weight: 670 g
- Dimensions: 280 × 216 × 15 mm
- Date of publishing: 04. October 2026
Osobný odber Bratislava a 13458 dalších
Copyright ©2008-26 najlacnejsie-knihy.sk Všetky práva vyhradenéSúkromieCookies

 25 miliónov titulov
 Vrátenie do mesiaca
 02/210 210 99 (8-15.30h)
