Kód: 54515717
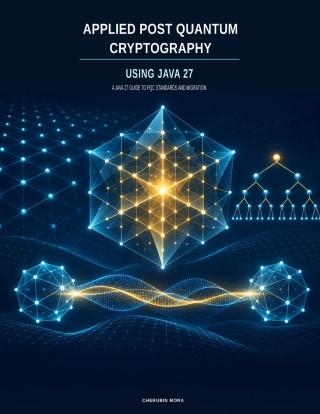
Applied Post Quantum Cryptography Using Java 27
Autor Cherubin Mora
Cryptographic migration takes years, while sensitive information may need protection for decades. Applied Post Quantum Cryptography Using Java 27 gives Java developers a practical guide to the quantum threat and the standards desi ... celý popis


- Jazyk:
 Angličtina
- Väzba: Brožovaná
- Počet strán: 108
Nakladateľ: Independently published, 2026
- Viac informácií o knihe

217.65 €
Bežne: 241.88 €
Ušetríte 24.24 €

Mohlo by sa vám tiež páčiť
-
Threshing Day (Limited Deluxe Edition)
21.02 € -29 % -
Cozy Countdown: An Advent Coloring Book Bundle
22.03 € -25 % -
Court of Thorns and Roses 6
17.22 € -15 % -
Murdoku
14.91 € -21 % -
White Nights
3.40 € -11 % -
Trust Fall
11.81 € -16 % -

A Conspiracy of Charming Monsters
17.12 € -25 % -
I'll Believe in Anything. The Making of Heated Rivalry Season 1
21.02 € -29 % -
The Mirror of Infinite Endings
17.92 € -17 % -

A Conspiracy of Charming Monsters
12.11 € -30 % -
Once Upon a Broken Heart Collector's Edition
27.53 € -23 % -
The Long-Lived King: An Original The Owl House Graphic Novel
19.72 € -16 % -

Chainsaw Man, Vol. 22
9.41 € -25 % -
Jojo's Bizarre Adventure: Part 7--Steel Ball Run, Vol. 9
19.32 € -21 % -
Berserk Deluxe Volume 1
47.17 € -11 % -
Protocols
20.22 € -24 % -
Murdoku Volume 2: Back in Time
13.71 € -29 % -
The End of Everything
14.21 € -22 % -
21 Days of Fear
17.72 € -22 % -
Threshing Day (Wing and Claw Collection)
18.52 € -25 % -
How to Win at Chess, Next Level
27.44 € -7 %
Darujte túto knihu ešte dnes
- Objednajte knihu a vyberte Zaslať ako darček.
- Obratom obdržíte darovací poukaz na knihu, ktorý môžete ihneď odovzdať obdarovanému.
- Knihu zašleme na adresu obdarovaného, o nič sa nestaráte.
Informovať o naskladnení knihy
Zadajte do formulára e-mailovú adresu a akonáhle knihu naskladníme, zašleme vám o tom správu. Postrážime všetko za vás.
Viac informácií o knihe Applied Post Quantum Cryptography Using Java 27
Nákupom získate 532 bodov
 Anotácia knihy

Cryptographic migration takes years, while sensitive information may need protection for decades. Applied Post Quantum Cryptography Using Java 27 gives Java developers a practical guide to the quantum threat and the standards designed to address it.
Explore ML-KEM key establishment, ML-DSA and SLH-DSA signatures, identity and certificate trust, hybrid key establishment, and TLS 1.3 integration. The examples use Java 27 JCA, JCE, and JSSE, with Bouncy Castle where needed. Symmetric encryption, hashing, and classical cryptography appear only to explain how PQC fits into deployed systems.
The book also covers PQC standards and algorithm status, provider and protocol support, certificate interoperability, harvest-now-decrypt-later risks, active attacks, and staged migration. Each example explains its assumptions and limits: a KEM does not authenticate a peer, algorithm availability does not establish module validation, and hybrid protocols must use defined combinations.
Written for developers comfortable reading Java, this book helps teams inventory quantum-vulnerable systems and prepare a safe, testable transition to post-quantum cryptography.
Parametre knihy
217.65 €
- Celý názov: Applied Post Quantum Cryptography Using Java 27
- Autor: Cherubin Mora
- Jazyk: Angličtina
- Väzba: Brožovaná
- Počet strán: 108
- EAN: 9798141699511
- ID: 54515717
- Nakladateľ: Independently published
- Hmotnosť: 368 g
- Rozmery: 280 × 216 × 7 mm
- Dátum vydania: 11. November 2026
Osobný odber Bratislava a 13485 dalších
Copyright ©2008-26 najlacnejsie-knihy.sk Všetky práva vyhradenéSúkromieCookies

 25 miliónov titulov
 Vrátenie do mesiaca
 02/210 210 99 (8-15.30h)
